Tesis sobre infraestructura,
regulación y verdad digital.
Análisis estratégico sobre gobernanza de IA, evidencia criptográfica y marcos regulatorios europeos — para equipos jurídicos, de compliance y dirección ejecutiva.
publicados
temáticas
DORA · NIS2
Inventario de sistemas de IA: guía práctica de compliance | V-PROOF
La mayoría de organizaciones que inician un programa de AI governance descubren el mismo problema: no saben exactamente qué sistemas de IA están usando. No de forma centralizada ni actualizada. Sin inventario no hay governance — y sin governance no hay compliance con el EU AI Act ni con ISO 42001.
Por qué tu herramienta de GRC no es suficiente para gobernar la IA y qué sí lo es
Los GRC no tienen capacidad de enforcement en tiempo real, no evalúan riesgo dinámico y no generan evidencia verificable de forma independiente. Descubre qué diferencia una plataforma real de AI Governance.
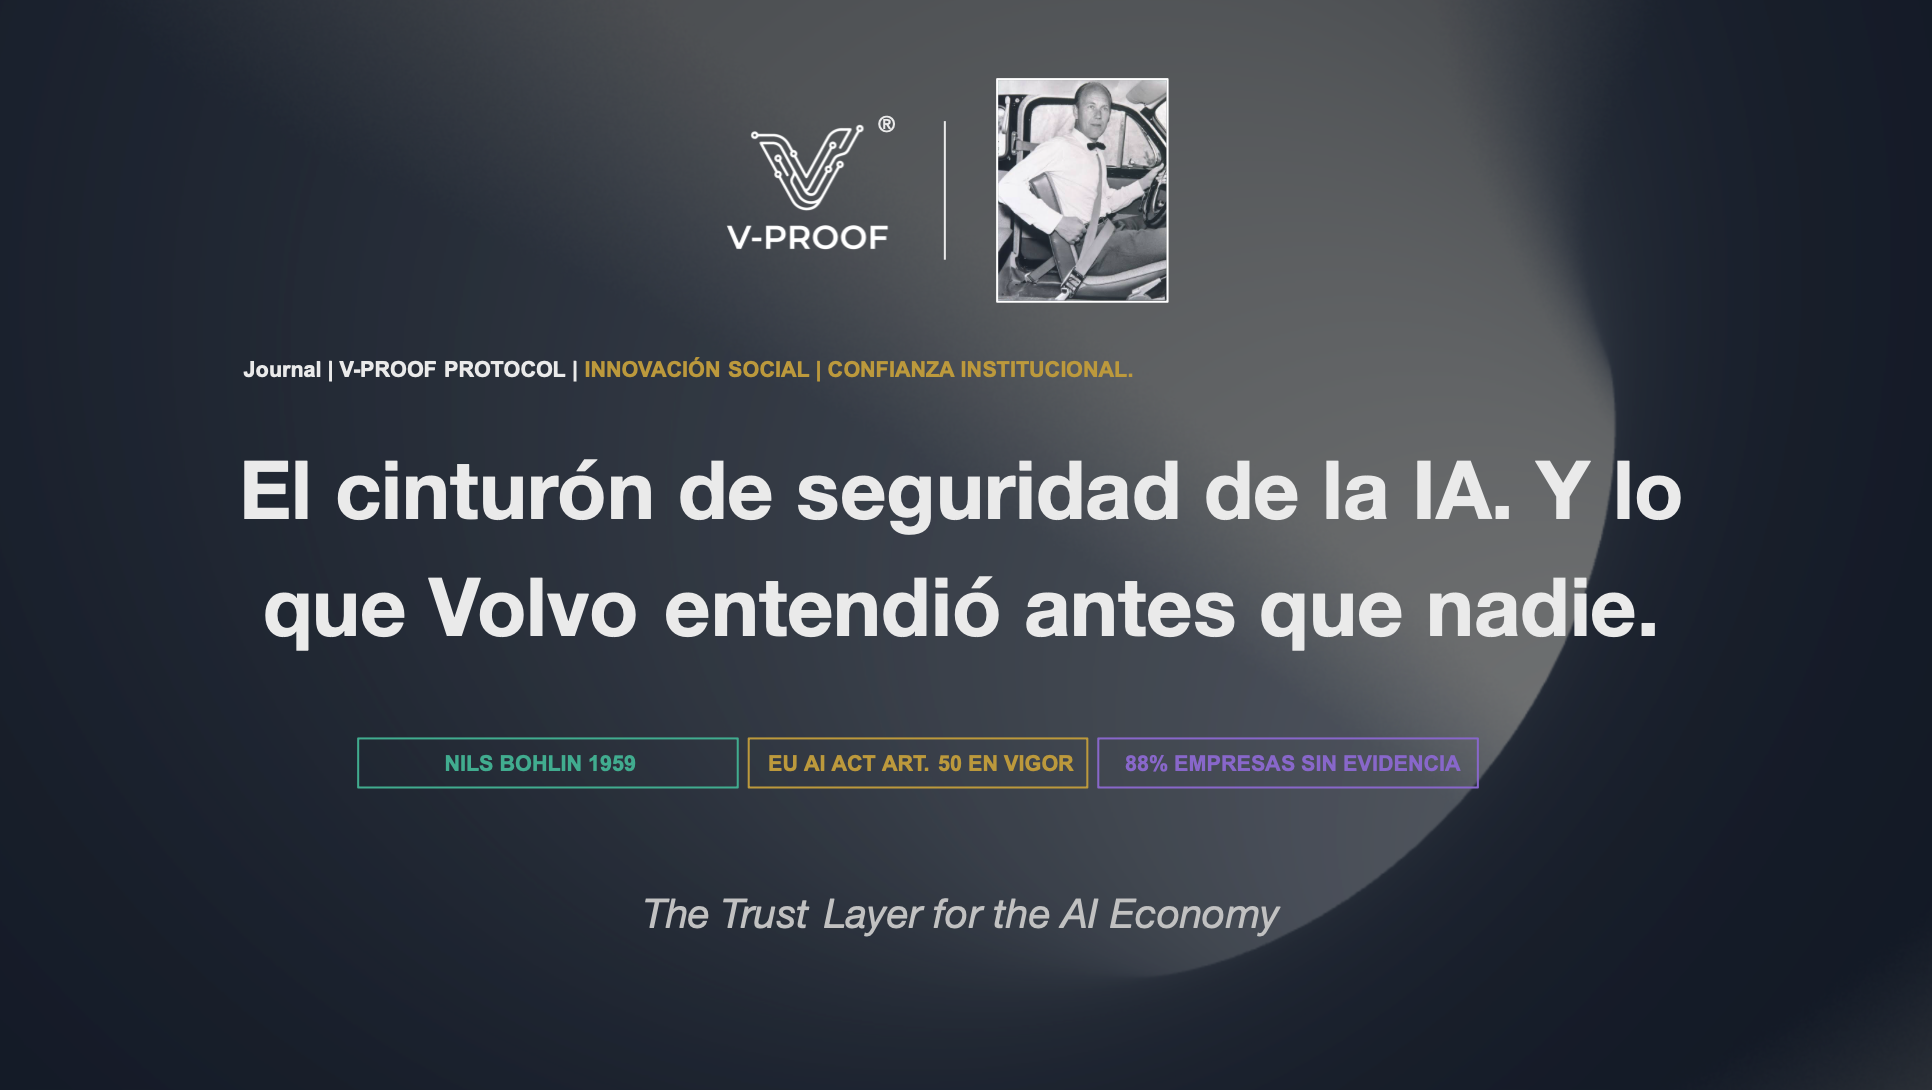
El cinturón de seguridad de la IA. Y lo que Volvo entendió antes que nadie.
En 1959, Nils Bohlin inventó algo que nadie había pedido. Volvo lo patentó y luego regaló la patente. No para ganar dinero — para que la confianza en el automóvil fuera un estándar universal. Hoy estamos en ese mismo momento con la IA. El problema no es tecnológico. Es de evidencia.
Por qué la infraestructura probatoria no es gobernanza de datos y la diferencia importa.
El mercado de la gobernanza de la IA está creciendo deprisa. Y con él, una confusión que tiene consecuencias reales. Cada semana aparecen plataformas que prometen "registros inmutables" y "compliance por construcción". Todas usan el mismo vocabulario. Pero no todas resuelven el mismo problema.
Governance as Code: el fin de los controles en documentos y el inicio de los guardrails ejecutables
Qué es Governance as Code, por qué los GRC no son suficientes para gobernar la IA y cómo V-PROOF implementa guardrails ejecutables en tiempo real sobre activos generados por inteligencia artificial.
2 de agosto de 2026: lo que cambia hoy para las organizaciones que usan IA de alto riesgo
El EU AI Act entra en vigor hoy para sistemas de IA de alto riesgo. No es una fecha de transición — es el inicio del periodo en el que las autoridades pueden investigar, requerir documentación y aplicar sanciones de hasta el 3% de la facturación global. Muchas organizaciones que llevan meses preparando su compliance descubrirán el mismo problema: sus registros actuales no generan la evidencia verificable que el Reglamento exige.
Gobernanza de IA: 30 preguntas clave, 8 marcos regulatorios, 1 capa de evidencia
Todos los marcos de gobernanza de IA — POPIA, ISO 42001, ISO 27001, ISO 27701, EU AI Act, NIST AI RMF, PCI DSS e HIPAA — definen el qué. Ninguno certifica el cómo ni el cuándo. Esta matriz cruza las 30 preguntas críticas de gobernanza contra los 8 estándares globales y añade la capa que faltaba: evidencia criptográfica verificable por cualquier auditor europeo. Compliance declarativo vs. compliance verificable.
La primera obligación del reglamento de IA.Y no es técnica. #ARTÍCULO 50 AI ACT
La primera obligación del EU AI Act no es técnica. El Artículo 50 entró en vigor el 2 de agosto de 2025 y exige a cualquier operador que usa IA informar de forma clara cuándo hay una máquina al otro lado. Análisis completo con marco legal, calendario y sanciones: hasta 15M€ o el 3% de facturación global.
El tren de los modelos fundacionales ya ha salido. Europa tiene otro.
La carrera de la inteligencia artificial no se gana únicamente con cómputo. Europa no compite en esa liga — y no tendría que intentarlo. Compite en otra: la confianza verificable, la soberanía jurídica y la capacidad de convertir la regulación en infraestructura estratégica. Opinión de Gil Blancafort, fundador de V-PROOF Protocol, publicada en Expansión (julio 2026).
La Vanguardia destaca la "caja negra" de la IA: V-Proof Protocol en el Especial Empresas
El incumplimiento puede costar hasta 35M€ o el 7% de la facturación global. La Vanguardia dedica un reportaje a V-Proof Protocol: la infraestructura nacida en Barcelona que convierte la supervisión humana de la IA en evidencia verificable, ante la EU AI Act que entra en vigor el 2 de agosto de 2026.
Why Your Organization Needs V-PROOF Than a Platform Based Outside the European Union
Of the 13 vendors in Gartner’s first AI Governance Magic Quadrant, none are based in the EU. We examine why using a platform outside the European Union to comply with the EU AI Act a structural legal contradiction—and what sets V-PROOF .
IPFS and Quantum Computing: Why the evidence you seal today with V-PROOF be valid in 2035
How V-PROOF decentralized architecture V-PROOF IPFS, SHA-256, and the NIST PQC roadmap to ensure that your digital evidence stands the test of time.
V-PROOF : Software Lifecycle Traceability in the Era of the EU Cyber Resilience Act
V-PROOF every commit, review, and production deployment—creating an auditable, immutable software supply chain that complies with the EU Cyber Resilience Act.
FFUUSS · OTS GROUP: AI Compliance Under Five Simultaneous ISO Certifications — Without a Single Nonconformity
FFUUSS · OTS GROUP: AI compliance with five ISO certifications + registered IP for all newly created digital assets.
"V-PROOF : The Trusted Infrastructure EU AI Act by the EU AI Act "
In less than two years, artificial intelligence has radically transformed corporate decision-making. But this revolution has brought with it an unprecedented challenge: regulatory risk. Faced with strict regulations such as the EU AI Act, the question echoing through boardrooms is clear: in the age of AI, how do you prove what is real, what is legal, and who created it?
Trust in the digital world can no longer rely on third parties or paper documents. Businesses need to prove their regulatory compliance instantly and with mathematical certainty. That is why we are announcing today the full rollout of V-Proof : the first Trust Layer Layer for the AI economy.
A new compliance standard designed to turn every corporate process and document into immutable evidence.
ROCADA: ISO 9001 traceability in an AI-assisted design process—version by version, without a single nonconformity.
AI-Driven Design Process + ISO 9001: How ROCADA Solved Document Traceability with V-PROOF. Zero nonconformities. Auditors verify via the QR code in seconds.
Enterprise Artificial Intelligence Now Has Its Own "Black Box"
Executive boards no longer have to choose between stifling innovation or exposing themselves to legal risks. We are pleased to announce the official launch of V-Proof , the first "black box" solution for enterprise AI that enables your teams to work with any large language model (LLM) while ensuring full compliance with the EU AI Act.
La prensa destaca la "caja negra" de la IA: V-Proof Protocol en El 9 Nou
Gil Blancafort and David Reifs are bringing the V-Proof vision to the media. From the in-depth report on El 9 Nou highlighting our corporate "black box" and recent financial momentum, to the interview on Catalunya Ràdio declaring the end of paper-based compliance. Discover how Hardcoded Compliance shields companies from the impending EU AI Act.
"Corporate AI needs a black box, not an ethics manual": V-Proof on Catalunya Ràdio
Gil Blancafort, CEO of V-Proof , visits Catalunya Ràdio to explain how companies can protect themselves against the new European AI Act. Find out why "paper-based compliance" is a thing of the past and why corporate artificial intelligence needs an immutable "black box" to ensure legal certainty and avoid fiduciary risks.

The Financial Times' Ultimatum: Why You Can't Blame AI for a Multi-Million-Dollar Failure—and the Urgency of Layer 0 Infrastructure.
The Financial Times warns: humans are the only ones legally liable for corporate AI failures. Find out why "Documentary Compliance" is a thing of the past and how V-PROOF your company from regulators through Hardcoded Compliance.